The Distinction between Cookies and Sessions
With a simple swap of a sweater, an online shopper might find her cart full of yesterday’s shoes. It isn’t wizardry, but a cookie or a session at work. Cookies and sessions use browser and server storage to remember pieces and interactions.
Web Browser Trinkets
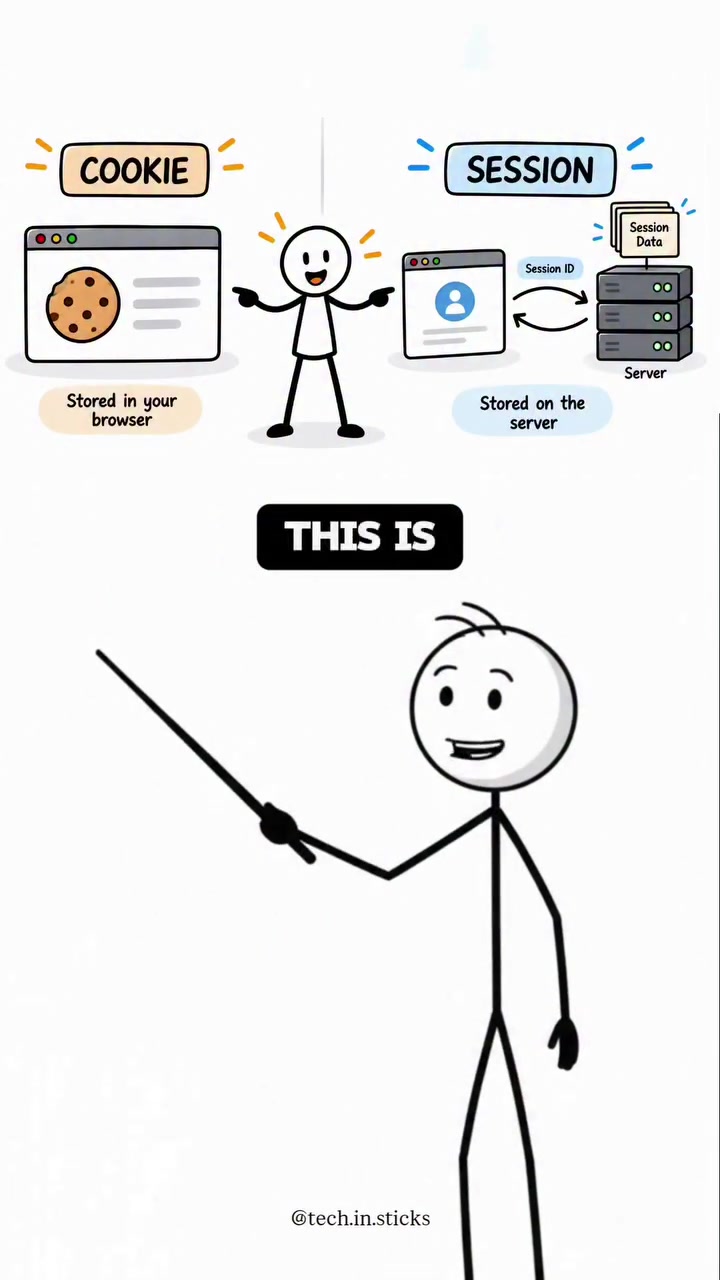
A cookie—a tiny data piece—resides in your browser. Imagine a digital note saying, “Remember these sneakers.” This note remains in your browser, along with other notes—cookies—and save your preferences and browsing details. The server doesn't keep this note. It’s stored in the user's browser. When stepping back into the browser’s note drawer, the cookie pops up and remembers what it held. Likewise, if you store a note in your digital drawer, it’ll be there next time. This note doesn’t need to be fancy: cookies can store only small pieces of data, like a username or a “remember me” flag for a login.
The Unseen Workhorse
When you log in to a website, it must remember who you are from page to page. This is where sessions come into play. Cookies can’t handle this alone. They don’t have the brainpower to keep you logged in by themselves. A session’s job is to remember that you’re logged in, and also track whether you move from the sneaker page to a new outfit. But here’s how it works: your browser usually keeps this session ID to help identify your session. Imagine every session as a unique marker. The session ID, the marker, can help the browser identify your current session. Your browser can’t store the data needed for authentication in a cookie. Only the server can authenticate the session. But the session ID in cookies can give the server a way to verify. It is a bridge.
The Storage Showdown: Where and Why
Cookies store data in the browser so you can remember items, preferences, and details across sessions. A session, on the other hand, stores data on the server, making it better suited for more sensitive tasks. Consider the differences as two different inboxes: the first, cookies, can store small bits of information in your browser; the second, sessions, is tucked away in the internet’s server closet.
The Content Check
When website can save information about your activities without storing all the sensitive information in cookies, people are less likely to encounter their personal information. The server handles the storage of the session ID, which is a more secure target for security. When a server uses sessions to verify you, it checks the Session ID stored in a cookie.
The Lifespan Difference
Sessions often expire quickly, usually after 20 or 30 minutes, but they might remain active as long as the session ID is valid. Cookies, depending on their type, can live on your browser for varying lengths of time, ranging from a few seconds to a few years. This dynamic lifespan between cookies and sessions provides a more nuanced approach to managing user data.
Shedding Light on the Browser vs. Server Debate
Which is better for keeping you logged in? The.cookie and the session work together to achieve this. The session ID in cookies is vital to maintaining a session. Though it’s nice to know how it works, you probably won’t need to manage sessions yourself. Once past the first login, the session stays active until logout. Every time you interact with a website, think about how many places store your data. Occasional interactions may not need your personal details. But important interactions like login details or paying for goods need to be stored securely. Each interaction’s security level depends on cookies and sessions working together.
The Shopper's Edge
Website cookies and sessions have lots of perks; the primary one is security. To keep track of everything, your browser should have a cookie to store smaller data. To keep everything secure, sessions will help to log you in and securely monitor those important things. Your browser keeps a session ID to help identify your session, and the server keeps the important session data.
- Tread Diligently: Be vigilant about the cookies on personal computers. Login’din to a public computer — log out.
- Know What They Need: Sites needing a login, monitor your security.
- Manage: Manage your cookies to ensure your security.
Questions readers ask
What's the main difference between cookies and sessions?
The main difference lies in where and how they store data. Cookies store small pieces of data, like preferences or usernames, directly in your browser. Sessions, on the other hand, store data on the server and use a session ID in a cookie to keep track of your login status and other sensitive information, like which pages you've visited.
Can cookies keep me logged in to a website?
Cookies alone can't keep you logged in. They can store a 'remember me' flag, but the actual authentication process is handled by sessions. The session ID stored in a cookie helps the server verify your login status.
Why are sessions more secure than cookies?
Sessions are more secure because they store sensitive data on the server rather than in the browser. This means that even if someone gains access to your cookies, they won't have your personal information. The server handles the session ID, providing an extra layer of security.
How do sessions and cookies work together to keep me logged in?
When you log in, a session is created on the server, and a session ID is stored in a cookie on your browser. This session ID acts as a bridge between your browser and the server, allowing the server to verify your login status and keep you logged in as you navigate the website.
How long do cookies and sessions typically last?
The lifespan of cookies can vary greatly, from a few seconds to a few years, depending on their type. Sessions, however, typically expire quickly, usually after 20 or 30 minutes, but can remain active as long as the session ID is valid. This difference in lifespan helps manage user data more effectively.
Can I delete cookies to log out of a website?
Deleting cookies can sometimes log you out of a website, but it's not guaranteed. If the website uses sessions, deleting the cookie containing the session ID might log you out. However, if the website uses other methods for authentication, simply deleting cookies might not be enough.
What happens if I clear my cookies while I'm still logged in?
If you clear your cookies while logged in, you might lose your session ID, which could log you out of the website. However, if the website uses other methods for authentication, you might still be logged in. It's always a good idea to log out properly before clearing your cookies to avoid any issues.
Related deep dives
Similar reads based on topic and creator.
Recent articles
Fresh deep dives from the latest Reels we unpacked.
Comments
Be the first to comment.