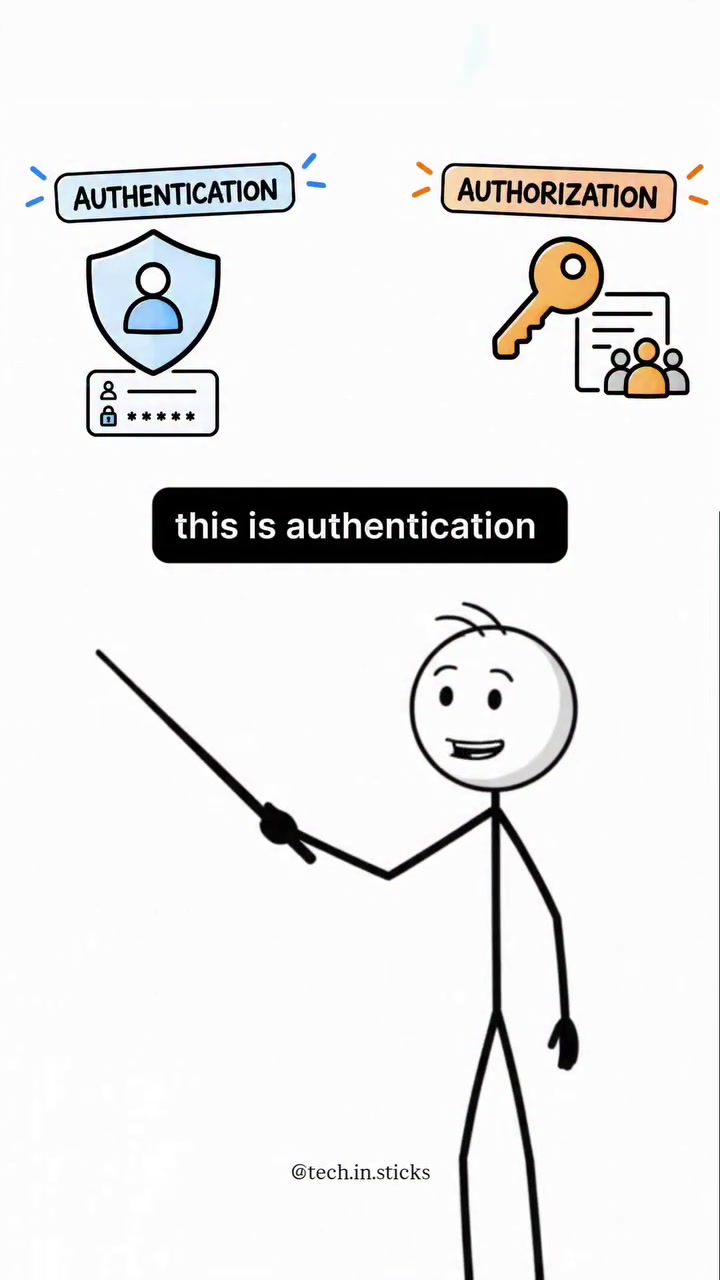
Digital Verification: The Dance of Authentication and Authorization
Authentication and authorization are two vital processes that underpin digital security. They sound similar but serve distinct purposes. Authentication verifies your identity — are you who you claim to be? Authorization, on the other hand, determines what you can access once your identity is confirmed. The process begins with authentication. Imagine logging into your social media account. You enter your email and password, and the system checks if you are indeed the account holder. This is identity verification. Authorization comes next. Even after logging in, you might not have access to all features or sensitive data. That's because authorization controls your permissions, deciding which parts of the system you can enter or interact with.
The Quest for Secure Access
In a world where digital interactions are ubiquitous, understanding these processes is crucial. From online banking to social media, from corporate networks to personal devices, authentication and authorization are the gatekeepers of our digital lives. As cyber threats evolve, so do the mechanisms to protect our data. Authentication is the first line of defense. It ensures that only authorized users can access a system. This is typically done through passwords, biometrics, or other verification methods. Authorization, meanwhile, manages what those verified users can do within the system. It’s about controlling access to specific resources or actions based on predefined permissions.
The Password Lock and Key
Authentication: Identity Check
Stick figures and diagrams may reduce complex ideas to simple visuals, but the concept is clear: authenticity is key. Authorization, on the other hand, is the process of determining what you can access or do once your identity is confirmed.
Authorization: Permission Granted
Once authenticated, the system checks your access rights. Think of it like entering an office building. Your ID card (authentication) gets you in the front door, but your access badge (authorization) decides which rooms you can enter.
The Office Analogy
To further illustrate, consider an office environment. Your ID card proves who you are; that's authentication. But your access permissions decide which rooms you can enter. You might have access to the break room but not the CEO’s office. This is authorization in action.
Step-by-Step Verification
Authorizing access to resources or actions within a system is like navigating an office building. Your ID card (authentication) opens the front door, but your access badge (authorization) determines which rooms you can enter. This analogy highlights the two-step process involved. Logging In: The simplest example to understand authentication is logging into any account. You enter credentials (email and password), and the system verifies your identity. Access Rights: Once logged in, authorization controls what you can do. For instance, a user might be able to view posts but not edit them. This is where authorization comes into play, deciding which permissions are granted based on the user's role or privileges.
Securing Your Digital Life — Understand and use them
Understanding these concepts will help you navigate the digital world more securely. Here are some practical steps to enhance your digital security:
- Choose Strong Passwords: Use a mix of letters, numbers, and special characters to create strong, unique passwords for each account.
- Enable Two-Factor Authentication (2FA): Whenever possible, enable 2FA to add an extra layer of security. This ensures that even if someone gets your password, they still need a second form of verification to access your account.
- Be Cautious with Permissions: Review and understand the permissions you grant to apps and services. Only provide the necessary access to keep your data secure.
- Regularly Update Credentials: Regularly change your passwords and update your authentication methods to reduce the risk of unauthorized access.
Questions readers ask
What's the main difference between authentication and authorization?
Authentication is all about verifying your identity—making sure you are who you claim to be. Authorization, on the other hand, determines what you can access or do within a system once your identity has been confirmed. For example, logging into your email account is authentication, but seeing only your own emails and not someone else's is authorization.
How do authentication and authorization work together in a typical login process?
When you log into a system, authentication is the first step. You enter your credentials, and the system verifies your identity. Once authenticated, authorization kicks in to determine what you can access based on your permissions. For example, after logging into a social media account, you might be able to view posts but not edit them, depending on your authorization level.
Can you give an example of authentication and authorization in everyday life?
Sure. Think of entering an office building. Your ID card is used for authentication—proving you are who you say you are. Once inside, your access badge determines which rooms you can enter, like the break room but not the CEO’s office. This is authorization in action, controlling what you can do within the secured area.
What are some common methods of authentication?
Common methods of authentication include passwords, biometrics (like fingerprints or facial recognition), and sometimes even physical tokens or security questions. These methods ensure that only authorized users can access a system by verifying their identity.
How does authorization control access within a system?
Authorization manages what authenticated users can do within a system. It’s based on predefined permissions. For example, in a social media platform, a regular user might be able to view and post content, but an admin might have additional permissions to delete posts or manage user accounts. This ensures that users can only access or perform actions they are authorized to.
What happens if someone fails authentication?
If someone fails authentication, it means they cannot prove their identity to the system. As a result, they won't be able to access the system at all. The system will typically deny entry and may prompt them to try again or use additional verification methods, like security questions or two-factor authentication, to confirm their identity.
Is it possible to have authorization without authentication?
No, authorization always follows authentication. You can't determine what someone can do within a system until you've first verified who they are. Think of it like trying to enter a restricted area without showing your ID—you won't get in, and you certainly won't be granted access to specific rooms within that area.
Related deep dives
Similar reads based on topic and creator.
Recent articles
Fresh deep dives from the latest Reels we unpacked.
Comments
Be the first to comment.