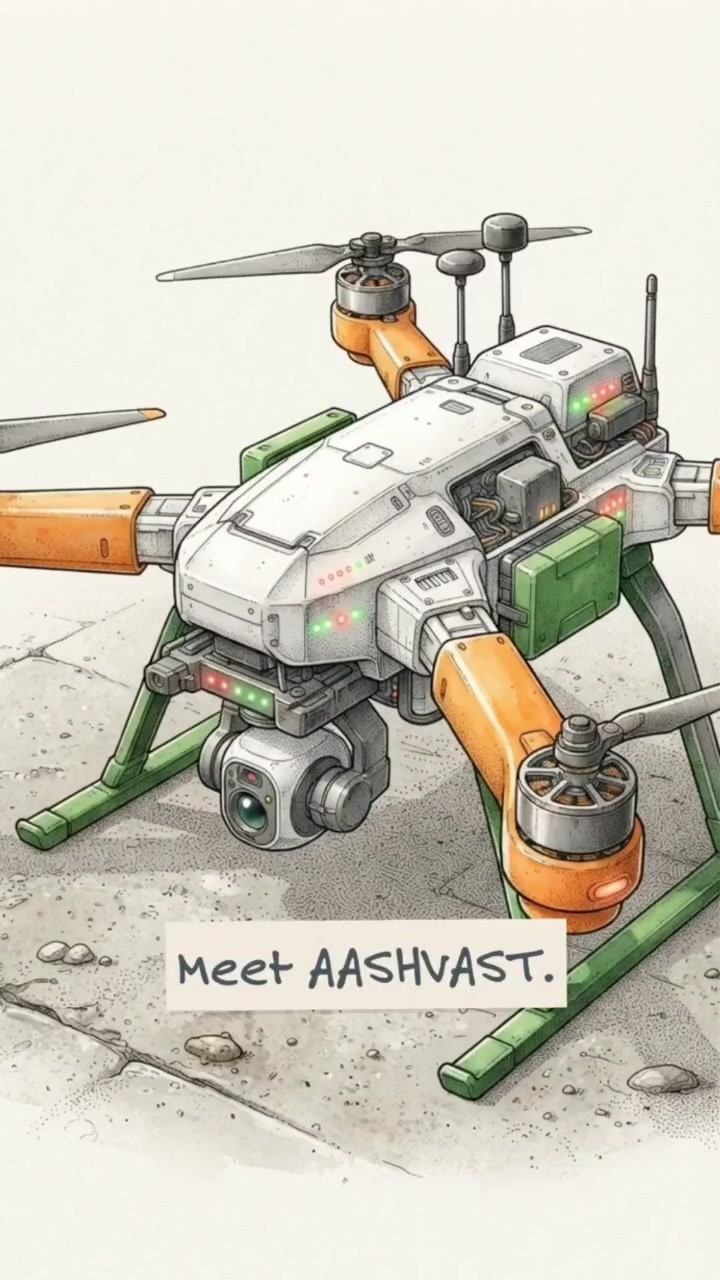
A newly imported military drone, designed to patrol a sensitive border, might seem secure, but what if its flight controller hides malicious code? That's the invisible danger the Indian Army addresses with Ashvost, a startup's unique weapon against hidden threats.
Inside Ashvost's non-intrusive chips
Ashvost, the Indian Army's answer to invisible threats, is designed to detect malicious code inside military drones and other electronics. To do so, Ashvost extracts the core operating software from the flight controller and pulls it into a secure lab. This environment, known as air-gapped, is completely disconnected from the internet. Air-gapping ensures that the software can be analyzed in complete isolation, preventing any external interference or potential remote hacking. By eliminating the possibility of remote access, this setup allows Ashvost to identify threats that standard tests would miss, such as malicious embedded code that activates at specific GPS coordinates. The delicacy of electronics extraction lies entirely with the human hand, making it a meticulous task but necessary to keep tech assets secure in the field, far from laboratory conditions. Once inside the secure lab, the software is scanned against 14 vulnerability categories, hunting for hidden encryption keys, remote access tools, and unauthorized command pathways. This thorough scanning ensures that no potential threat goes unnoticed.
A national security leap, far from VC fuelled tech
Ashvost is developed by QuickPayTech, a Noida-based startup led by director Rajiv Roy. While other tech innovations often thrive on massive VC valuations, Ashvost is solving crucial national security problems with less fanfare and high-impact results. As the Indian Army continues to expand its use of drones and other electronic devices in sensitive border patrols, Ashvost’s unique approach ensures that every piece of tech hardware remains secure—including battlefield CCTV cameras. The methodology, known as "trust the electronics," emphasizes the need for secure tech, particularly in a world where electronic espionage is a constant threat.
The unseen warfare around embedded code
At the heart of Ashvost's mission is a foundational rule of electronic warfare: malicious code can stay hidden, not activated until it reaches a specific GPS location. This scenario makes it all the more crucial to have a system like Ashvost, which can physically extract and analyze the core operating software from any electronic device. Once inside the secure lab, the software undergoes a rigorous scan to detect any potential threats. This includes the examination of encryption keys, remote access tools, and unauthorized command pathways. With the ability to detect malicious embedded code, Ashvost ensures that any potential threat to national security is identified and neutralized long before it can cause any damage.
The deeper scan: 14 threat categories
The software within the air-gapped lab is meticulously scanned against 14 distinct vulnerability categories, bolstering security by ensuring no angle of vulnerability goes unchecked. This process ensures the identification of hidden encryption keys, remote access tools, and unauthorized command pathways. By scrutinizing every facet, Ashvost remains vigilant against a wide array of threats, including:
- Encryption keys: Hidden keys that may allow unauthorized access to data and functions.
- Remote access tools: Tools that could allow an attacker to take control of the electronics.
- Unauthorized command pathways: Pathways that can bypass security protocols and be exploited by malicious actors.
Identifying the silent intruders: foreign code
The electronic invisibility of foreign code complicates threat detection. While the physical motors of a military drone are straightforward to inspect for any foreign material, the untraceable chips that house the electronic navigation, operating, and security systems are another story. These chips can harbor foreign code, designed to stay dormant until triggered by specific GPS coordinates. This threat is particularly dangerous because standard flight tests and inspections won't reveal it. By extracting the core operating software from the flight controller and analyzing it in an air-gapped lab, Ashvost can identify these hidden threats before they activate.
Get started
While Ashvost is notably ahead of the game and first to market, especially in national security, its findings may soon be translated into everyday tech. It's not yet clear how or if it can be bought, but consumers and enterprises aren't off the hook for hidden threats in electronics.
- Learn about air-gapping: Research the concept of air-gapping, especially practical examples for your business or home. The more you know, the better you can implement the methodology.
- Pay attention to vulnerabilities: While Ashvost scans 14 distinct categories, you can start by paying attention to the invisible threats found in commonly used electronics, such as encryption keys and remote access tools. Subscribe to news outlets and industry publications that follow tech vulnerabilities.
- No physical inspection is foolproof: Understand that just as Ashvost emphasizes the physical extraction of core operating software, even the most rigorous inspections of hardware may not reveal hidden threats—especially in the rapidly evolving world of electronics.
Related deep dives
Similar reads based on topic and creator.
Recent articles
Fresh deep dives from the latest Reels we unpacked.
Comments
Be the first to comment.